Last month, I volunteered myself to run a breakout session at the 2012 UAS Conference, an annual gathering of up to a thousand Oxford University staff. I'd run a 2-minute micropresentation at the July 2011 OxLibTeachMeet called "Your Password Sucks!", and I thought I'd probably be able to expand that into a larger 25-minute breakout session.
Alt
Your password: How bad guys will steal your identity
The essence of my presentation boiled down to demonstrating four points. The first was you are a target - dispelling the myth that the everyday person can consider themselves safe from the actions of malicious hackers. I described the growth of targeted phishing attacks, and relayed the sad story of Mat Honan's victimisation by hackers.
The second point was that your password is weak: I described the characteristics of good passwords (e.g. sufficiently long, complex, random, and unique) and pointed out that even among folks who'd gotten a handle on most of these factors, uniqueness was still the one that tripped people over. A quarter of people use only a single password for most or all of their accounts, and over 50% use 5 or fewer passwords across dozens of accounts.
Alt
You are a target. Your password is weak. Attacks are on the rise. You can protect yourself.
Next up: attacks are on the rise. By a combination of statistics, anecdotes, audience participation and a theoretical demonstration of how a hacker might exploit shared-password vulnerabilities to gradually take over somebody's identity (and then use it as a platform to attack others), I aimed to show that this is not just a hypothetical scenario. These attacks really happen, and people lose their money, reputation, or job over them.
Finally, the happy ending to the story: you can protect yourself. Having focussed on just one aspect of password security (uniqueness), and filling a 25-minute slot with it, I wanted to give people some real practical suggestions for the issue of password uniqueness. These came in the form of free suggestions that they could implement today. I suggested "cloud" options (like LastPass or 1Password), hashing options (like SuperGenPass), and "offline" technical options (like KeePass or a spreadsheet bundles into a TrueCrypt volume).
I even suggested a non-technical option involving a "master" password that is accompanied by one of several unique prefixes. The prefixes live on a Post-It Note in your wallet. Want a backup? Take a picture of them with your mobile: they're worthless without the master password, which lives in your head. It's not as good as a hash-based solution, because a crafty hacker who breaks into several systems might be able to determine your master password, but it's "good enough" for most people and a huge improvement on using just 5 passwords everywhere! (another great "offline" mechanism is Steve Gibson's Off The Grid system)
Alt
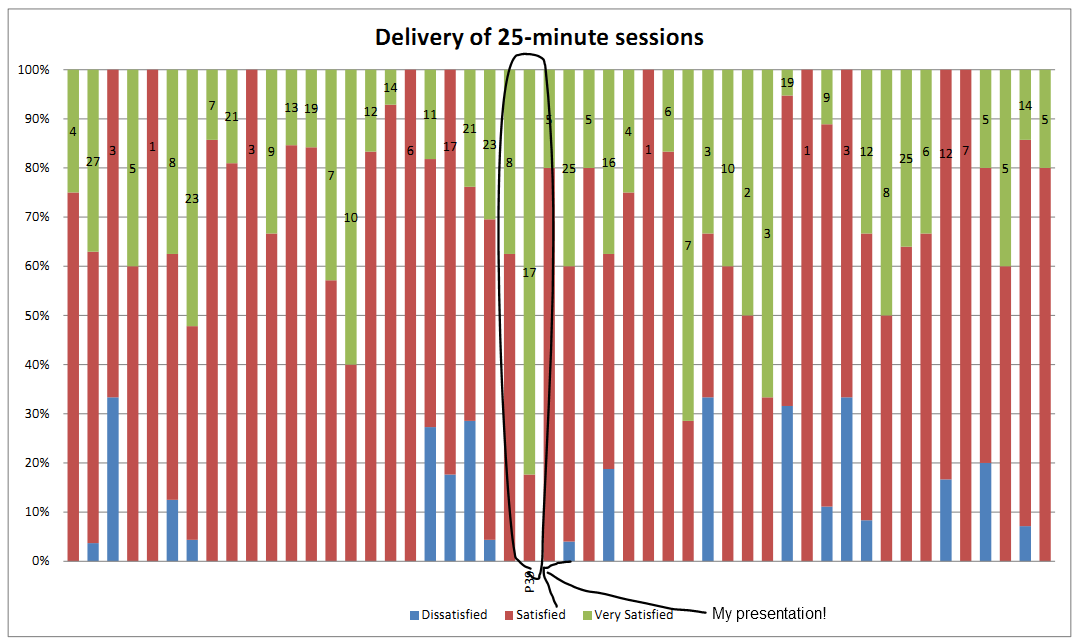
"Delivery" ratings for the UAS Conference "breakout" sessions
And it got fantastic reviews! That pleased me a lot. The room was packed, and eventually more chairs had to be brought in for the 70+ folks who decided that my session was "the place to be". The resulting feedback forms made me happy, too: on both Delivery and Content, I got more "Very Satisfied" responses than any other of the 50 breakout sessions, as well as specific comments. My favourite was:
Best session I have attended in all UAS conferences. Dan Q gave a 5 star performance.
So yeah; hopefully they'll have me back next year.
0 comments