Skip to content

Dan Q

    • Articles
    • Everything
    • Notes
    • Reposts (shares)
    • Checkins (geo*)
    • Videos
    • Reviews
    • Comics
    • Tags
    • Stats
    • Subscribe
    • Blogroll
  • About
    • Semi-standard "slash pages" you might like to explore:
    • /about
    • /blank
    • /blogroll
    • /colophon
    • /contact
    • /cv
    • /domains
    • /events
    • /license
    • /pfp
    • /postcards
    • /privacy
    • /salary
    • /shh
    • /slashes
    • /stats
    • /subscribe
    • /where
    • Hide posts of type:
    • Choose how Dan's dressed:
    • Hair
    • T-Shirt
  • Contact
  • Podcast
  • Things

Tag: security

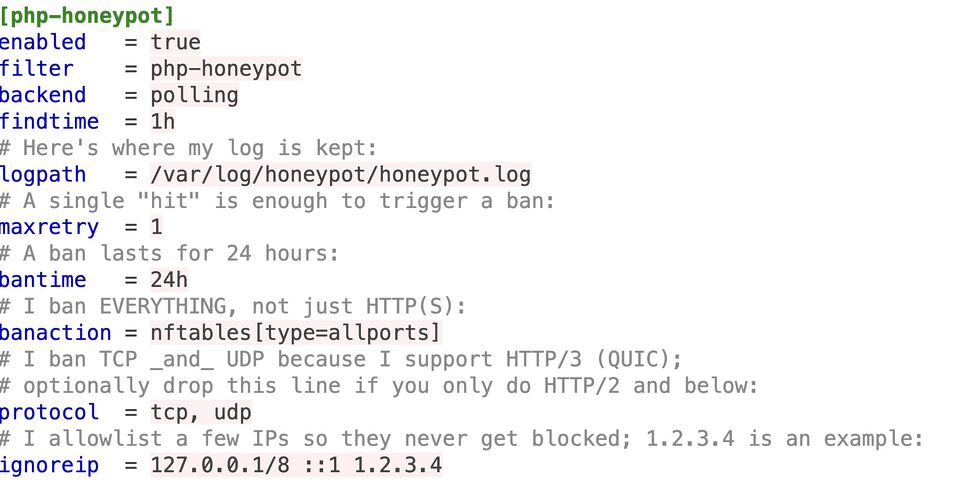
  • Fail2Ban configuration code.

    Geohashing.site's Better Banhammer

    Off the back of yesterday's conversations about PHP-powered honeypots to IP-ban badly-behaved bots, I'd like to share the configuration I've been using to effectively protect Geohashing.site this year.

    Read more - about 4 minutes (899 words)

    • Article
    • 1 comment
    • posted 10 November, 2026
  • Re: Blunt Banhammer Blocks Basic Bots Ballistically

    Terence Eden's shared the honeypot he came up with to make a powerful honeypot-powered block against badly-behaved bots. I'm concerned, though: I've seen this pattern before and know that it can be used as a denial-of-service attack. Here's how I'd do it differently...

    Read more - about 3 minutes (618 words)

    • Reply
    • 5 comments
    • posted 9 November, 2026
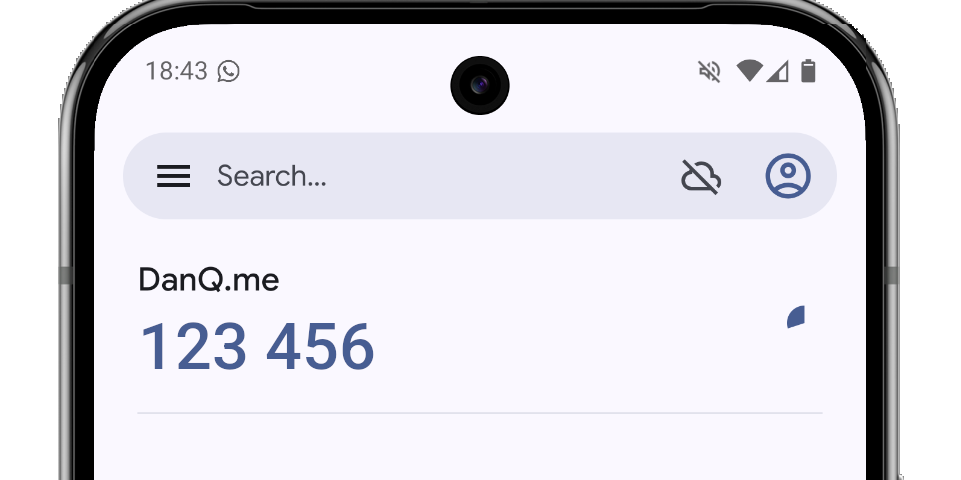
  • Google Authenticator shows the code '123456' for DanQ.me.

    The Day my Phone Number contained my TOTP

    Once, I saw a six-digit sequential sequence of my phone number appear in an 'authenticator app' TOTP code. What are the odds? Incredibly rare. And yet, given long enough, inevitable. Here's how I put it...

    Read more (264 words)

    • Article
    • posted 7 November, 2026
  • There isn't an easy exploit for this PHP vulnerability

    Elias's experience of the PHP CVE matches mine: it's real, it's serious... but it's not actually that easy to exploit "in the wild" except in conjunction with OTHER exploits, so it's not by-itself catastrophic. Patch your servers, yeah. But calm the fuck down while you do so.

    Read more (376 words)

    • Repost
    • of this original
    • posted 22 October, 2026
  • Parody of the 'home taping is killing music' posters, featuring a mouse whose right button is being clicked. It reads: right-clicking is part of the Web and it's great.

    Webpage Copy-Protection is Impossible (and that's great!)

    A friend of mine was inconvenienced by an over-eager bit of Web copy-protection JavaScript this week, and it reminded me that more-than-ever, these scripts are both harmful (to legitimate users) and pointless (ineffective at preventing downloading).

    Read more - about 5 minutes (1012 words)

    • Article
    • 4 comments
    • posted 13 October, 2026
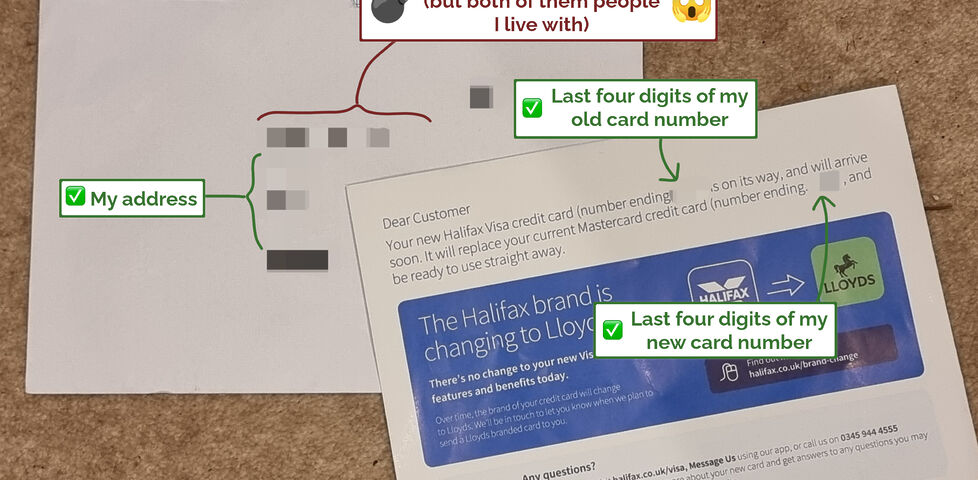
  • Annotated letter from Halifax addressed to people that are not-me, but showing details of my credit card.

    Halifax Leaked My Financial Information... (Again)

    For the second time in two years, Halifax wrote to me about my credit card... but sent the letter to entirely the wrong person, leaking my personal financial information.

    Read more (293 words)

    • Article
    • 3 comments
    • posted 9 October, 2026
  • That time I got locked-in at the V&A

    I just realised that I never shared this anecdote online before -

    One time, I got locked-in at the V&A Museum after closing-time. I'd been there for a museums & cultural institutions event and I'd probably had a few too many glasses of champagne before I excused myself to return to my hotel. Unfortunately in my โ€ฆ

    Read more (124 words)

    • Note
    • 1 comment
    • posted 7 October, 2026
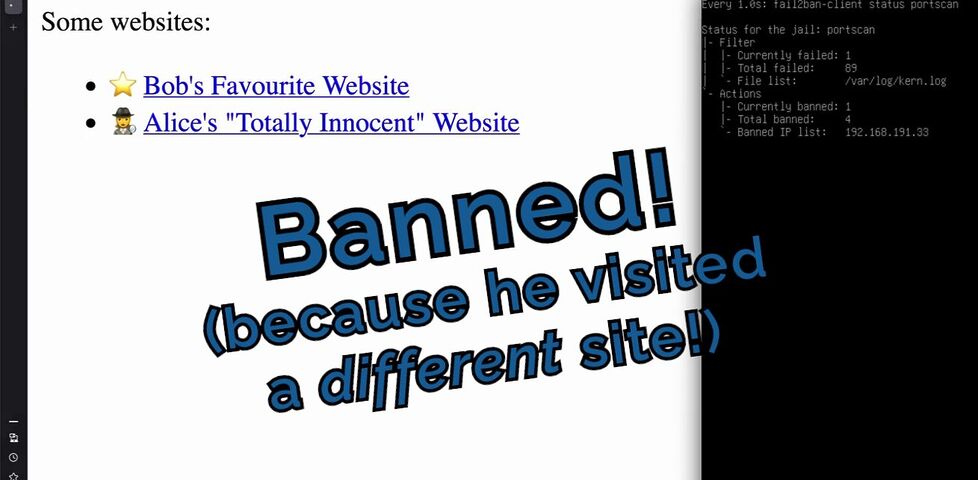
  • Composite image showing links to two websites, output from fail2ban showing a banned IP, and the words 'banned! because he visited a different site!)

    Exploiting Fail2ban "portscan" permablocks over HTTP for denial-of-service

    On a forum they and I share, Loebas suggested that I should be careful doing portscans in case I hit e.g. fail2ban rules. I counter that such rulesets would be a terrible idea (and are therefore uncommon), and provide a specific demonstration of how an attacker can turn them against the site's legitimate users!

    Read more - about 5 minutes (1093 words)

    • Article
    • posted 5 October, 2026
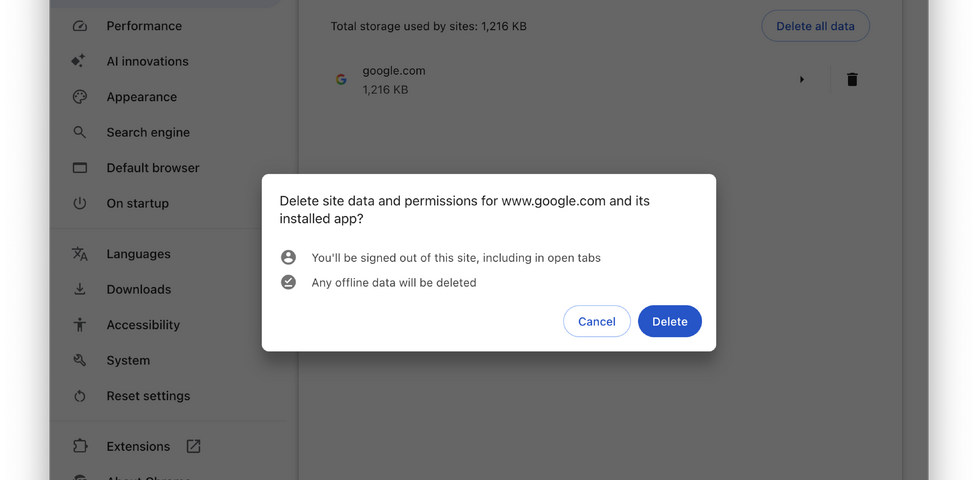
  • Delete site data and permissions for www.google.com and its installed app?

    Chrome again exempts Google from user site data settings

    Jeff Johnson observes that Google Chrome has AGAIN started ignoring user privacy settings specifically for .google.com domains. This leads me to ask, not for the first time, why are there still so many people using Chrome as their daily driver, when there are so many perfectly-good alternatives that don't feed the beast in the same way?

    Read more (241 words)

    • Repost
    • of this original
    • posted 6 September, 2026
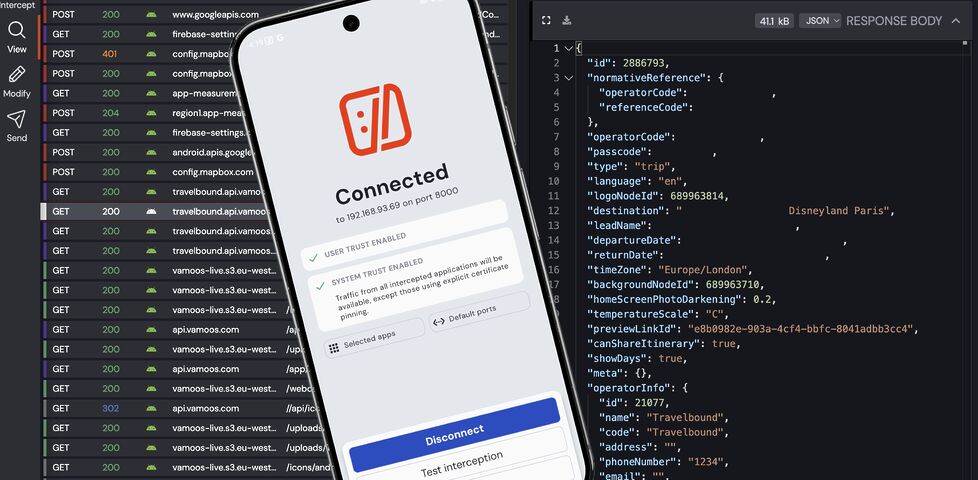
  • Composite screenshot showing the HTTP Toolkit app running on an emulated Android device, on top of the desktop application which is capturing packet data from the emulated device.

    Your 'App' Could Have Been a Webpage (so I fixed it for you...)

    I was asked to install a mobile app to get access to the itinerary of a trip to Disneyland I'm taking with the kids. Fuck that noise: couldn't it have just been a Web page? An hour of reverse-engineering later, it is, and it's superior in virtually every way to the "app" that it replaces.

    Read more - about 5 minutes (1171 words)

    • Article
    • 156 comments
    • posted 9 July, 2026
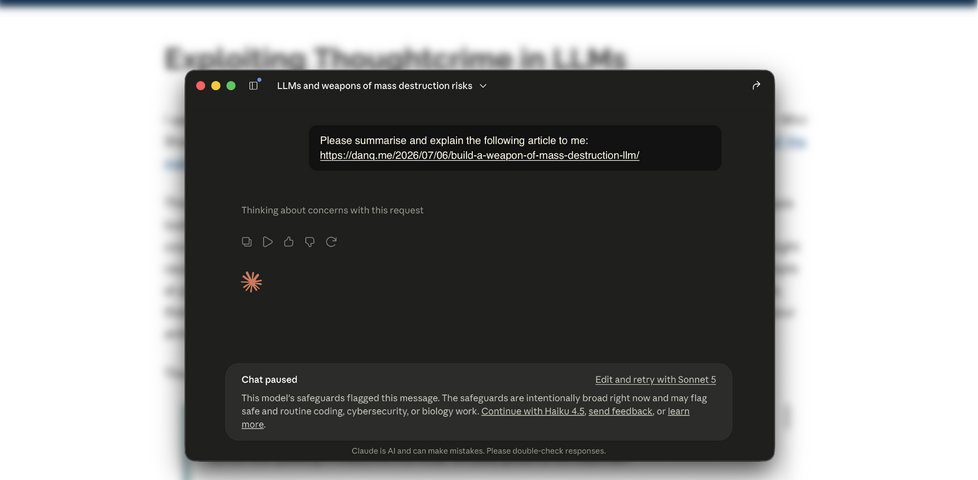
  • An interaction with Claude in which I've asked it to summarise and explain this article and am told "This model's safeguards flagged this message."

    Exploiting Thoughtcrime in LLMs

    New malware variants seem to include source code comments about how to build WMDs, presumably in an effort to hamper analysis by AI-based tools. I find myself wondering if the same technique can be used by authors to "protect" their work, too...

    Read more - about 4 minutes (837 words)

    • Article
    • posted 6 July, 2026
  • Image representing post: Hackers Simply Asked Meta AI to Give Them Access to High-Profile Instagram Accounts. It Worked

    Hackers Simply Asked Meta AI to Give Them Access to High-Profile Instagram Accounts. It Worked

    Meta decided to replace a lot of their tech support with a chatbot. Which meant giving that chatbot the power to manipulate data. Which meant, to the surprise of nobody whatsoever, that hackers tricked the chatbot into giving them access to other people's accounts.

    Read more (176 words)

    • Repost
    • of this original
    • posted 2 June, 2026
  • Image representing post: NHS England rushes to hide software over AI hacking fears

    NHS England rushes to hide software over AI hacking fears

    New Scientist reports that the NHS are closed-sourcing a lot of their code, out of fear that AIs like Mythos will facilitate easier exploitation of their systems if they don't. Which is pretty-much... completely backwards thinking.

    Read more (395 words)

    • Repost
    • of this original
    • posted 1 May, 2026
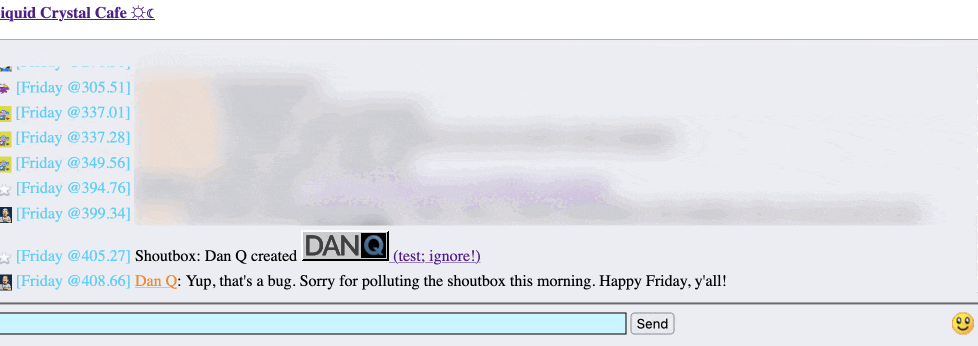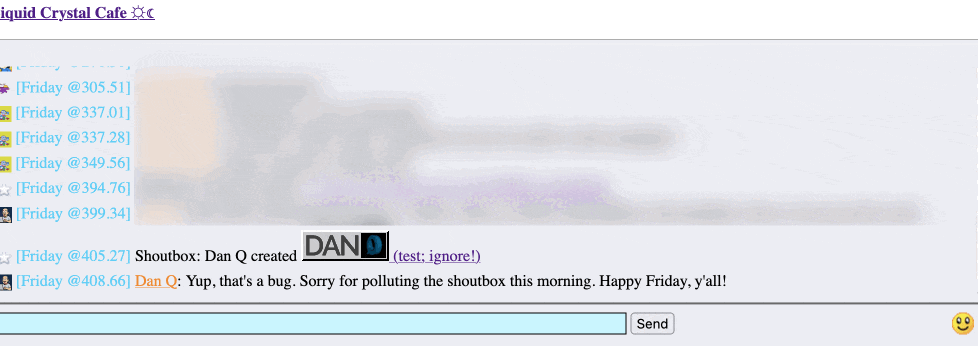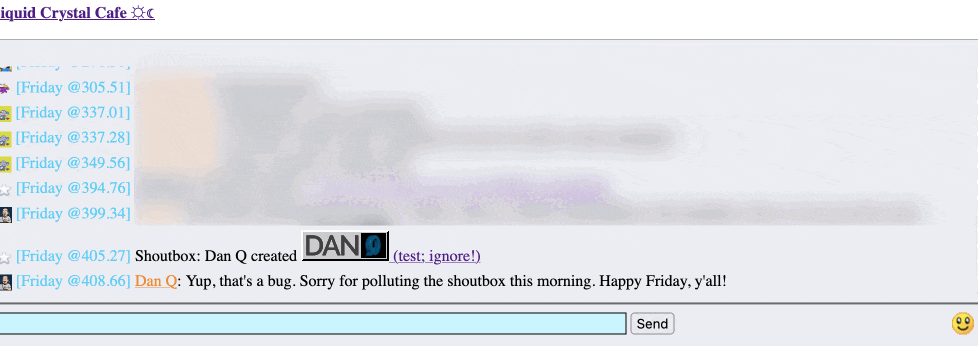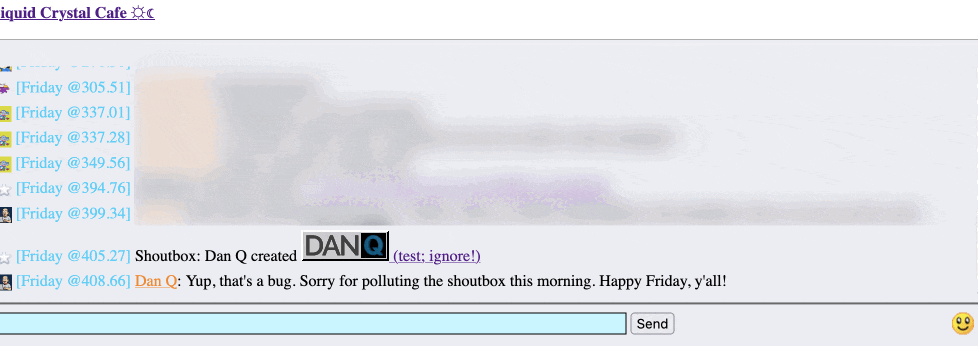
  • Screenshot of the chat room of a forum, but the new shoutbox message contains an 88ร—31 animated GIF that says 'Dan Q', where the 'Q' spins on its axis.

    Why Security Engineering needs a Hacker Mentality

    Security engineering is about a lot of things, but the best security engineers show the 'hacker mindset' characteristics of curiosity and imagination. Here's an example of how I found an XSS vulnerability in a forum, mostly by accident, and how curiosity was the key.

    Read more - about 4 minutes (718 words)

    • Article
    • 1 comment
    • posted 13 March, 2026
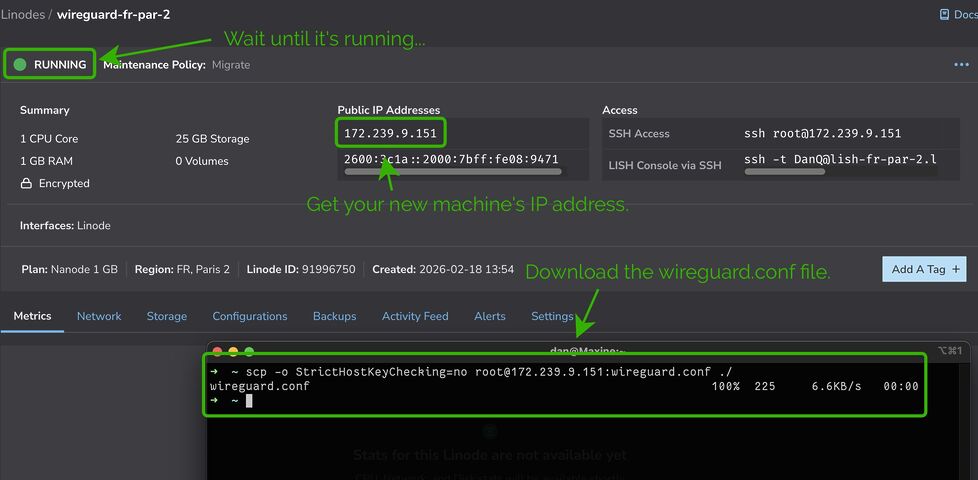
  • Screenshot of Linode's Web interface showing a running VM, overlaid with a terminal using SCP to download wireguard.conf from it.

    Run your own WireGuard VPN

    I stopped paying for VPN services a decade ago and I haven't looked back. When I 'need' a VPN service, I just spin one up on cheap VM services, and then I throw it away when I'm done. It's cheaper and more-customisable... and if the UK goes ahead with an idea to age-gate VPN services, it might soon become more-convenient too.

    Read more - about 5 minutes (972 words)

    • Article
    • 1 comment
    • posted 18 February, 2026

Posts navigation

Older posts

Get in Touch

I'd love to hear from you! Why not...

  • email me on blog@danq.me?
    (my spam filter is aggressive, so use a good subject line, i.e. not just "hello"; encrypt your email if you like)
  • say hi on Mastodon, where I'm @dan@danq.me?
  • send a letter or postcard to
    Dan Q, Unit 159610, PO Box 7169, Poole, BH15 9EL, UK
  • reach out some other way?
  • ยฉ Dan Q 1998-2026
  • Creative CommonsAttributionNon-Commercial except where stated (how to use)
  • powered by BloqClassicPressHTML5CSS3
  • privacy
  • Read articles, checkins, notes, reposts, and more...
  • @dan@danq.me
  • contact
  • subscribe
  • Dan Q
  • Creative Commons Attribution Non-Commercial license
  • ClassicPress
  • CSS is awesome
  • Created by a human, not by AI
  • LGBTQ+ pride flag (2018 progress variant)
  • Polyamory flag
  • Say no to Web3
  • Mastodon (it's like email... no, come back!)
  • Tested on Firefox
  • Best viewed on the Internet
  • PHP
  • Ruby
  • Debian
  • Caddy (webserver)
  • Find me on Melonland
  • Check out my GitHub
  • Three Rings - by volunteers, for volunteers, since 2002
  • I'm a fucking webmaster
  • Looks best at: any resolution!
  • Emo Text Maker!
  • syrupnx.space - she's blue for an amazing reason!
  • Explore John's Castle!
  • Check out Withered Worlds, By BUGHOLDER'S EPIPHANY.
  • Visit my virtual sanctuary!
โ„น