Tag: security
-
Brainfart
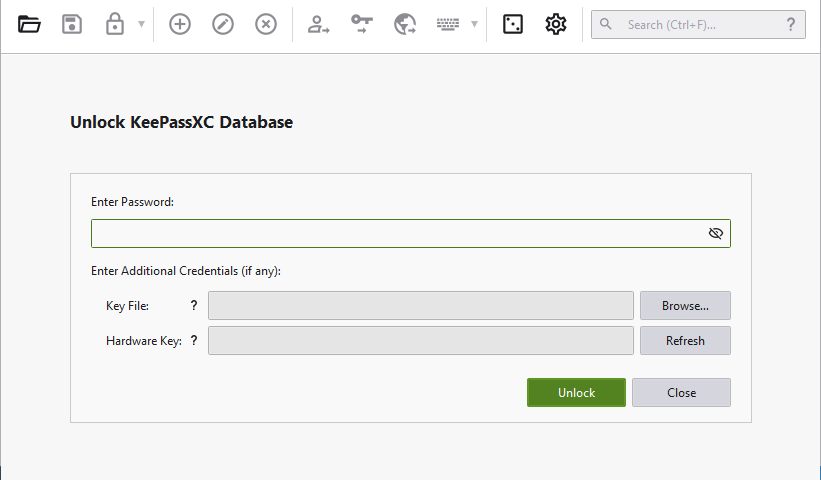
Brainfart moment this morning when my password safe prompted me to unlock it with a password, and for a moment I thought to myself "Why am I having to manually type in a password? Don't I have a password safe to do this for me?" 🤦
-
Length Extension Attack Demonstration (Video)
This is a video version of my blog post, Length Extension Attack. In it, I talk through the theory of length extension attacks and demonstrate an SHA-1 length extension attack against an (imaginary) website.
The video can also be found on:
YouTube
-
Length Extension Attack Demonstration
Hash length extension attacks aren't necessarily intuitive without a little understanding of how vulnerable hashing algorithms work. Using SHA1 as an example, I've put together a step-by-step demonstration with a focus on teaching the underlying principles behind the vulnerability.
-
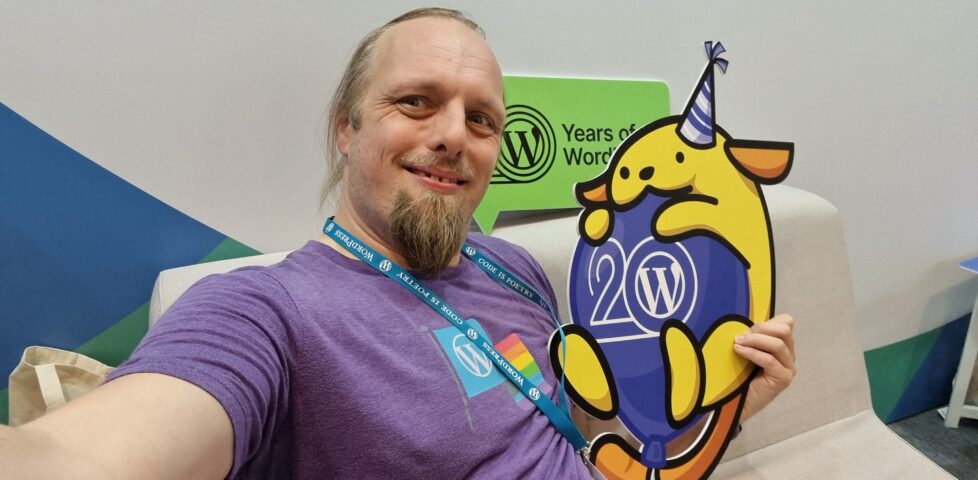
WCEU23 - Day 1
My first "full" day at WordCamp Europe 2023 was busy and intense, but I loved networking and learning about WordPress history and security and what's worth knowing about design and typography.
-
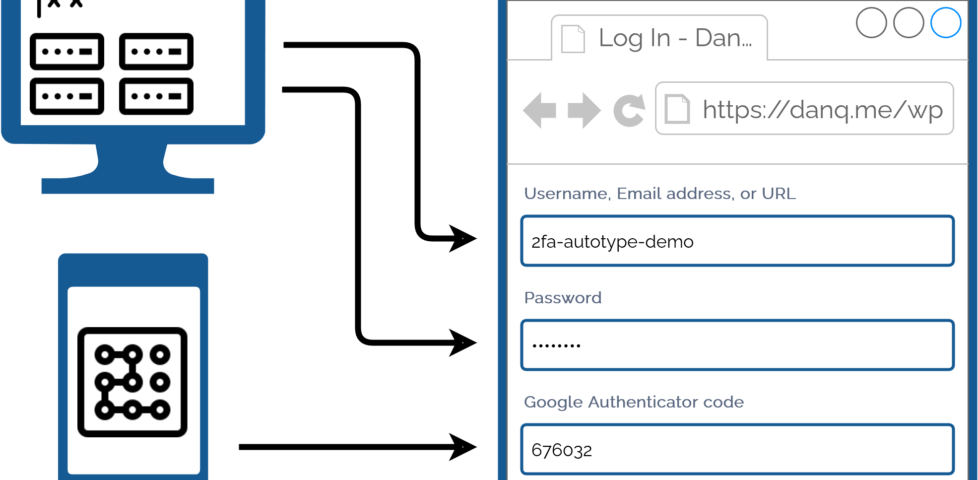
Keeping 2FA Secrets in a Password Safe?
I use my password manager to generate TOTP second factor codes. I know this is controversial, with some folks claiming it reduces multifactor authentication down to a single factor and is therefore no better than just a username/password, but I disagree, and I can explain why.
-
I'd Like to Change my Mother's Maiden Name
LastPass users are having to cycle their passwords in the light of a recent security incident. That might well include their "security question" answers, which necessarily leads to some amusing conversations.
-
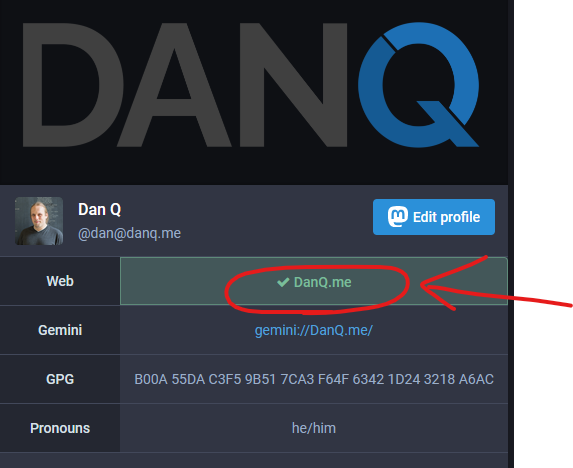
Reply to Decentralization and verification
Dan replies to Derek Kedziora's blog post, arguing that identity verification on Mastodon is, for the most part, a problem already solved.
-
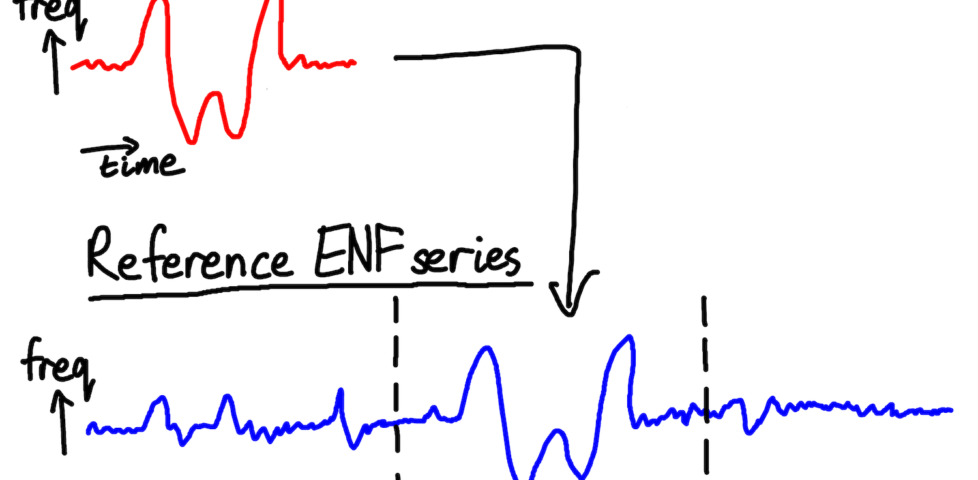
How to date a recording using background electrical noise
Robert Heaton shares some specifics of EMF forensics, and Dan reconsiders an idea he had years ago for a hardware spoofer.
-
Hey @VOXI_UK! There's a security #vulnerability in your website. An attacker can (a) exfiltrate mobile numbers and (b) authenticate bypassing OTP.
Not sure who to talk to about ethical disclosure. Let me know? -
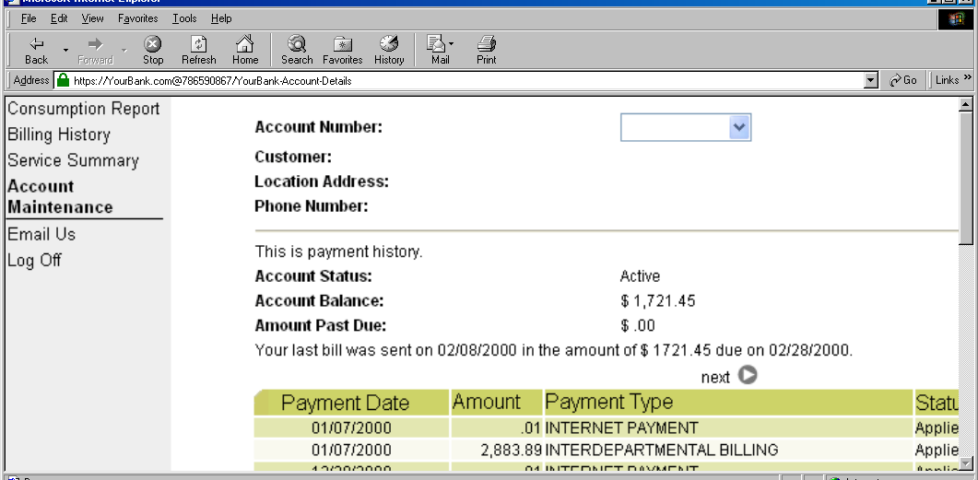
Can I use HTTP Basic Auth in URLs?
Dan dives into HTTP Basic Authentication, its history, and how modern browsers support it, with a focus on URL-based credential passing.
-
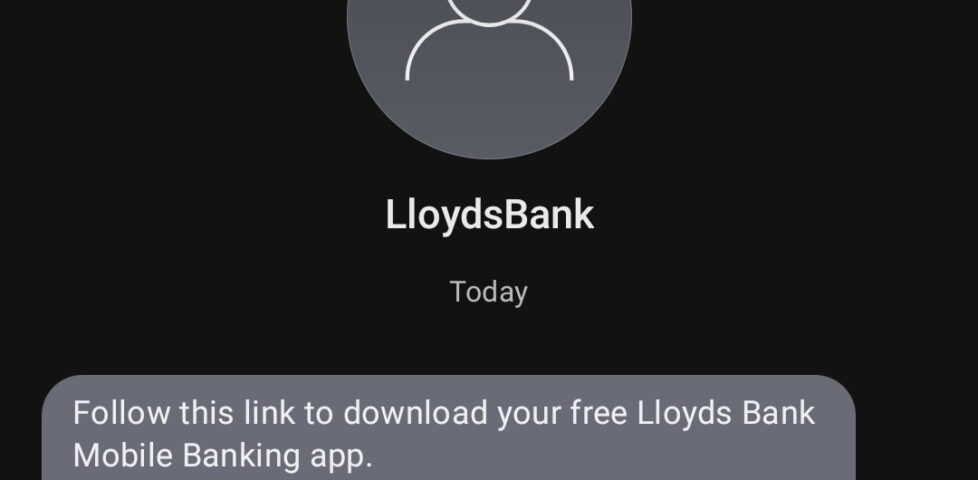
Hey @LloydsBank! 2009 called and asked if you're done sending your customers links to unencrypted HTTP endpoints yet. How do you feel about switching this to a HTTPS link rather than relying on an interceptable/injectable HTTP request?
-
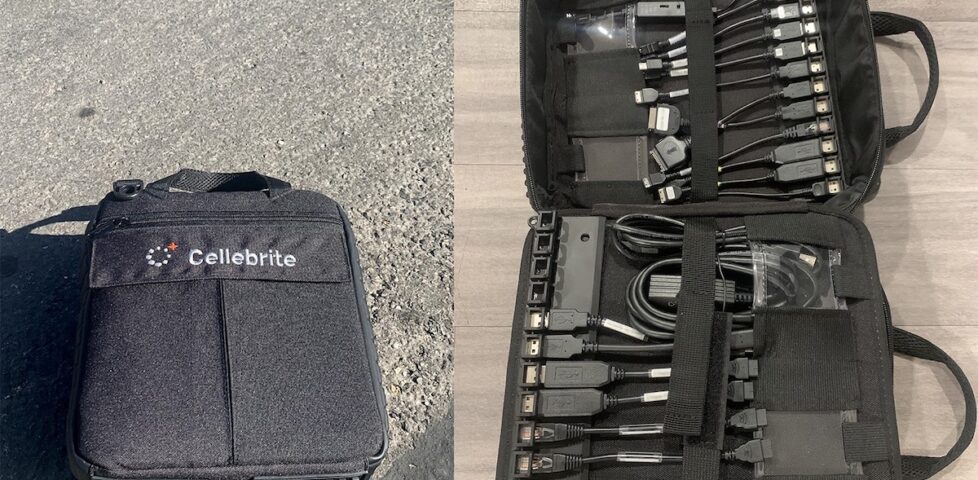
Exploiting vulnerabilities in Cellebrite UFED and Physical Analyzer from an app's perspective
Moxie Marlinspike "acquires" a Cellebrite UFED and hacks it, with all the delight and sarcasm you'd expect. Dan partially-translates.
-
Big List of Naughty Strings
# Reserved Strings
#
# Strings which may be used elsewhere in code
undefined
undef
null
NULL
...
then
constructor
\
\\
# Numeric Strings
#
# Strings which can be interpreted as numeric
0
1
1.00
$1.00
1/2
1E2
...
Max Woolf
Max has produced a list of "naughty strings": things you might try injecting into your systems along with any fuzz testing you're doing to check for common errors in escaping, processing, casting, … -
Why using Google VPN is a terrible idea
Google are launching a VPN service. The Proton team say why that's bad, and Dan takes a more-sarcastic look at the issue.
-
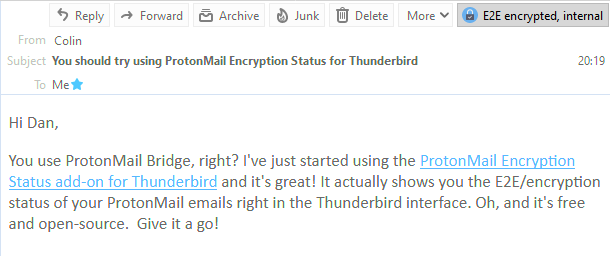
Displaying ProtonMail Encryption Status in Thunderbird
Dan releases his first Thunderbird plugin, for improving integration with ProtonMail Bridge.