Tag: security
-
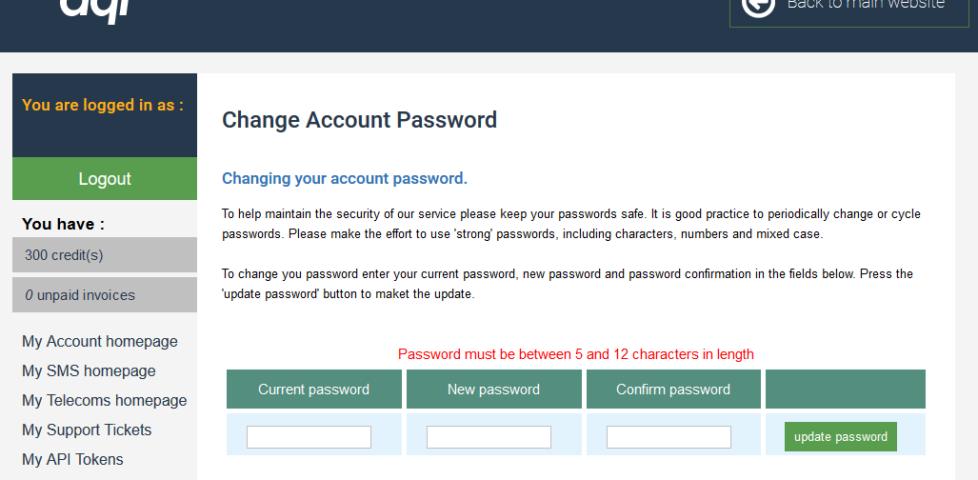
Hey @aqldotcom: why must my password for your enterprise telecommunications platform be no longer than 12 characters? Are you worried my #passwordistoostrong? CC @pwtoostrong -
#youbroketheinternet So We Got Tracked Anyway
Did you install EFF's brilliant Privacy Badger or any other smart HTTP Cookie management tool? Or did you simply pick the privacy preference in your browser that ignores all third-party cookies? Did many websites you visit annoy you with permission-to-use-cookies pop-ups because of European legislation?
Guess what, it's all been useless.
Hamburg university researchers … -
There is no longer any such thing as Computer Security
Remember "cybersecurity"? Mysterious hooded computer guys doing mysterious hooded computer guy .. things! Who knows what kind of naughty digital mischief they might be up to? Unfortunately, we now live in a world where this kind of digital mischief is literally rewriting the world's history. For proof of that, you need look no further than…
… -
Five-Eyes Intelligence Services Choose Surveillance Over Security
The Five Eyes -- the intelligence consortium of the rich English-speaking countries (the US, Canada, the UK, Australia, and New Zealand) -- have issued a "Statement of Principles on Access to Evidence and Encryption" where they claim their needs for surveillance outweigh everyone's needs for security and privacy. ...the increasing use and sophistication of certain…
… -
What Cyber-War Will Look Like
When prompted to think about the way hackers will shape the future of great power war, we are wont to imagine grand catastrophes: F-35s grounded by onboard computer failures, Aegis BMD systems failing to launch seconds before Chinese missiles arrive, looks of shock at Space Command as American surveillance satellites start careening towards the Earth--stuff …
-
Dot-dash-diss: The gentleman hacker's 1903 lulz
A century ago, one of the world’s first hackers used Morse code insults to disrupt a public demo of Marconi's wireless telegraph
AltNevil Maskelyne – doing it for the lulz?
LATE one June afternoon in 1903 a hush fell across an expectant audience in the Royal Institution’s celebrated lecture theatre in … -
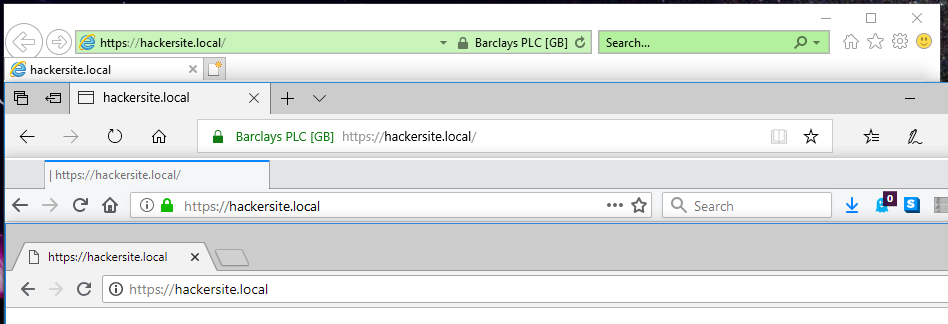
How Edge Follows In IE's Security Failings
Replicating an experiment Steve Gibson performed into browser EV certificate acceptance, Dan discovers that an ugly security-weakening "feature" of Internet Explorer also appears in Edge. What the hell, Microsoft?
-
Before You Turn On Two-Factor Authentication
Many online accounts allow you to supplement your password with a second form of identification, which can prevent some prevalent attacks. The second factors you can use to identify yourself include authenticator apps on your phone, which generate codes that change every 30 seconds, and security keys, small pieces of hardware similar in size … -

Intercepting HTTPS Traffic from Android Emulator
A brief guide to decrypting HTTPS traffic sent to/from Android apps.
-
Quantum Key Distribution Whitepaper
https://www.ncsc.gov.uk/whitepaper/quantum-key-distribution (ncsc.gov.uk) This white paper describes our current position on quantum key distribution (QKD). QKD is an approach to key distribution that relies on the properties of quantum mechanics to provide security. ...
For all the practical, business and security reasons given above, at this point in time we:
do not endorse QKD for any … -
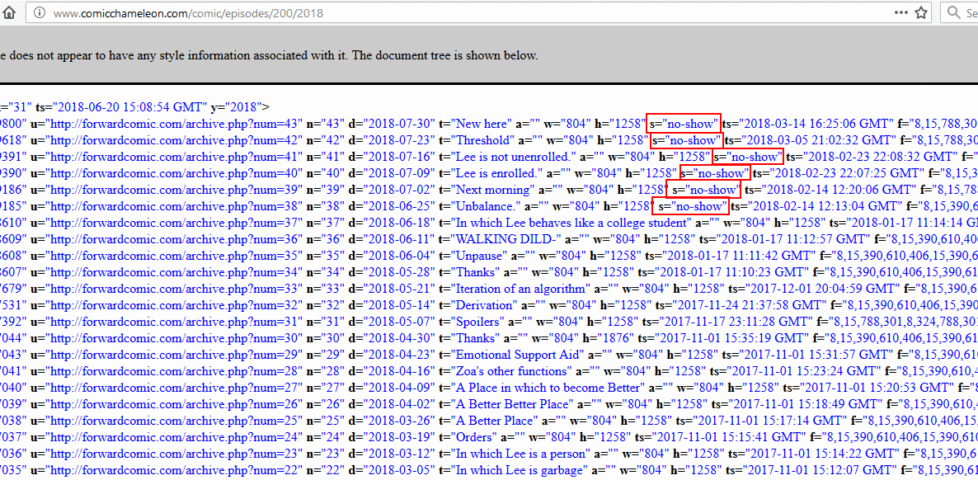
Leak in Comic Chameleon (app API hacking)
Not for the first time, Dan becomes an "accidental hacker" when he finds a bug in a comic-reader app that lets him read not-yet-published episodes of a webcomic he follows.
-
Unbreakable smart lock devastated to discover screwdrivers exist
https://www.theregister.co.uk/2018/06/15/taplock_broken_screwdriver/ (theregister.co.uk) It's never easy to crack into a market with an innovative new product but makers of the "world's first smart fingerprint padlock" have made one critical error: they forgot about the existence of screwdrivers.
Tapplock raised $320,000 in 2016 for their product that would allow you to use just your finger to open the … -
No, Panera Bread Doesn't Take Security Seriously
No, Panera Bread Doesn’t Take Security Seriously – PB – Medium by an author (Medium) tl;dr: In August 2017, I reported a vulnerability to Panera Bread that allowed the full name, home address, email address, food/dietary… tl;dr: In August 2017, I reported a vulnerability to Panera Bread that allowed the full name, home address, email …
-
After Section 702 Reauthorization
After Section 702 Reauthorization - Schneier on Security (schneier.com) For over a decade, civil libertarians have been fighting government mass surveillance of innocent Americans over the Internet. We've just lost an important battle. On January 18, President Trump signed the renewal of Section 702, domestic mass surveillance became effectively a permanent part of US law. …
-
My Blog Now Has a Content Security Policy - Here's How I've Done It
My Blog Now Has a Content Security Policy - Here's How I've Done It (Troy Hunt) I've long been a proponent of Content Security Policies (CSPs). I've used them to fix mixed content warnings on this blog after Disqus made a little mistake, you'll see one adorning Have I Been Pwned (HIBP) and I even …