Tag: security
-
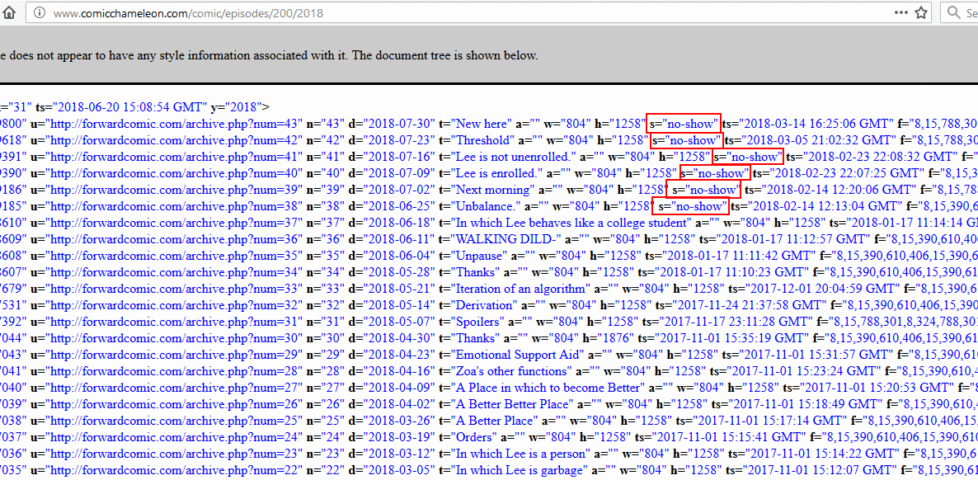
Leak in Comic Chameleon (app API hacking)
Not for the first time, Dan becomes an "accidental hacker" when he finds a bug in a comic-reader app that lets him read not-yet-published episodes of a webcomic he follows.
-
Unbreakable smart lock devastated to discover screwdrivers exist
https://www.theregister.co.uk/2018/06/15/taplock_broken_screwdriver/ (theregister.co.uk) It's never easy to crack into a market with an innovative new product but makers of the "world's first smart fingerprint padlock" have made one critical error: they forgot about the existence of screwdrivers.
Tapplock raised $320,000 in 2016 for their product that would allow you to use just your finger to open the … -
No, Panera Bread Doesn't Take Security Seriously
No, Panera Bread Doesn’t Take Security Seriously – PB – Medium by an author and an author (Medium) tl;dr: In August 2017, I reported a vulnerability to Panera Bread that allowed the full name, home address, email address, food/dietary… tl;dr: In August 2017, I reported a vulnerability to Panera Bread that allowed the full name, …
-
After Section 702 Reauthorization
After Section 702 Reauthorization - Schneier on Security (schneier.com) For over a decade, civil libertarians have been fighting government mass surveillance of innocent Americans over the Internet. We've just lost an important battle. On January 18, President Trump signed the renewal of Section 702, domestic mass surveillance became effectively a permanent part of US law. …
-
My Blog Now Has a Content Security Policy - Here's How I've Done It
My Blog Now Has a Content Security Policy - Here's How I've Done It (Troy Hunt) I've long been a proponent of Content Security Policies (CSPs). I've used them to fix mixed content warnings on this blog after Disqus made a little mistake, you'll see one adorning Have I Been Pwned (HIBP) and I even …
-
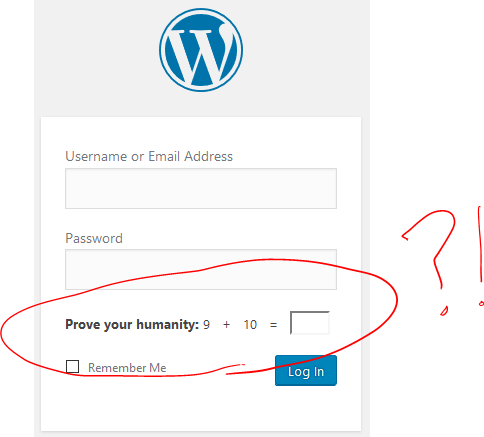
Bypassing WordPress / Jetpack's "Prove your humanity:" CAPTCHA
Popular WordPress plugin Jetpack provides a CAPTCHA whose sole purpose seems to be to frustrate humans. It does nothing to stop bots, as Dan demonstrates with a browser plugin that circumvents it.
-
Security Breaches Don't Affect Stock Price
Security Breaches Don't Affect Stock Price - Schneier on Security (schneier.com) false Interesting research: "Long-term market implications of data breaches, not," by Russell Lange and Eric W. Burger. Abstract: This report assesses the impact disclosure of data breaches has on the total returns and volatility of the affected companies' stock, with a focus on the …
-
I'm harvesting credit card numbers and passwords from your site. Here's how.
I’m harvesting credit card numbers and passwords from your site. Here’s how. (hackernoon.com) false
It’s been a frantic week of security scares — it seems like every day there’s a new vulnerability. It’s been a real struggle for me personally to pretend like I understand what’s going on when asked about it by family … -
Secure Messaging Apps Comparison
SecureMessagingApps.com
This site maintains a table cross-referencing the most popular "secure" messaging apps (WhatsApp, Signal, Skype etc.) against their security features, so that you can make an informed decision.
The tl;dr is, of course, what I've been saying all along: use Signal! (at least until Riot is more mature...) -
"I Forgot My PIN": An Epic Tale of Losing $30,000 in Bitcoin
In January 2016, I spent $3,000 to buy 7.4 bitcoins. At the time, it seemed an entirely worthwhile thing to do. I had recently started working as a research director at the Institute for the Future’s Blockchain Futures Lab, and I wanted firsthand experience with bitcoin, a cryptocurrency that uses a blockchain to record transactions …
-
A hacker stole $31M of Ether - how it happened and what it means for Ethereum
Yesterday, a hacker pulled off the second biggest heist in the history of digital currencies.
Around 12:00 PST, an unknown attacker exploited a critical flaw in the Parity multi-signature wallet on the Ethereum network, draining three massive wallets of over $31,000,000 worth of Ether in a matter of minutes. Given a couple more hours, the hacker … -
Password Rules Are Bullshit
Of the many, many, many bad things about passwords, you know what the worst is? Password rules.
If we don't solve the password problem for users in my lifetime I am gonna haunt you from beyond the grave as a ghost pic.twitter.com/Tf9EnwgoZv
— Jeff Atwood (@codinghorror) August 11, 2015
Let this pledge be duly … -
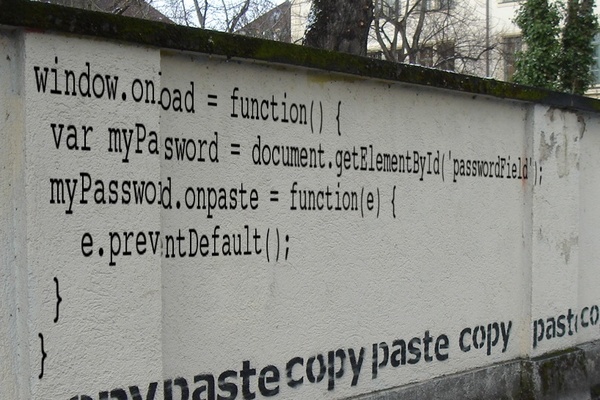
Let them paste passwords
One of the things people often tweet to us @ncsc are examples of websites which prevent you pasting in a password. Why do websites do this? The debate has raged - with most commentators raging how annoying it is.
So why do organisations do this? Often no reason is given, but when one is, that reason … -
A Russian Slot Machine Hack Is Costing Casinos Big Time
In early June 2014, accountants at the Lumiere Place Casino in St. Louis noticed that several of their slot machines had—just for a couple of days—gone haywire. The government-approved software that powers such machines gives the house a fixed mathematical edge, so that casinos can be certain of how much they’ll earn over the long … -
Defeating Quantum Algorithms with Hash Functions
In this post I’ll explain why quantum computers are useless to find hash function collisions, and how we can leverage this powerlessness to build post-quantum signature schemes. I’ll then describe a quantum computing model that you can try at home, and one where hash function collisions are easy to find...
JP Aumasson (Kudelsi Security)