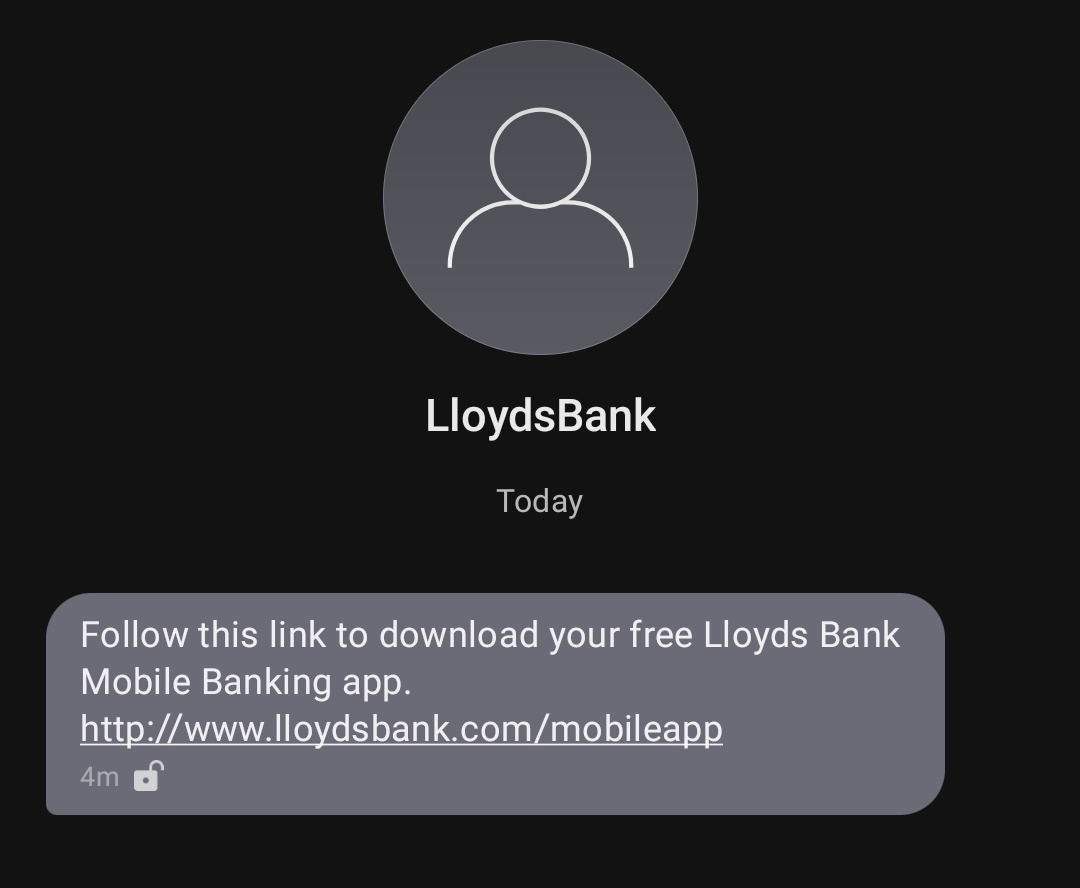
Hey @LloydsBank! 2009 called and asked if you're done sending your customers links to unencrypted HTTP endpoints yet. How do you feel about switching this to a HTTPS link rather than relying on an interceptable/injectable HTTP request?
Alt
Text message: "Follow this link to download your free Lloyds Bank Mobile Banking app. http://www.lloydsbank.com/mobileapp"
@LloydsBank They don’t even have HSTS set up: https://t.co/Hndp6eGewd
They have it on HTTPS, and always redirect to HTTPS, so they're half-trying.