Tag: security
-
TLS 1.3 FTW
In common slang, FTW is an acronym "for the win" and while that's appropriate here, I think a better expansion is "for the world."
We're pleased to announce that we have sponsored the development of TLS 1.3 in OpenSSL. As it is one of the most widely-used TLS libraries, it is a good investment for the … -
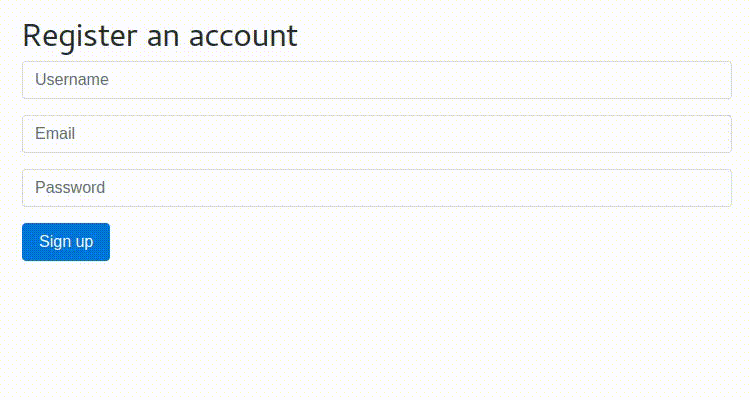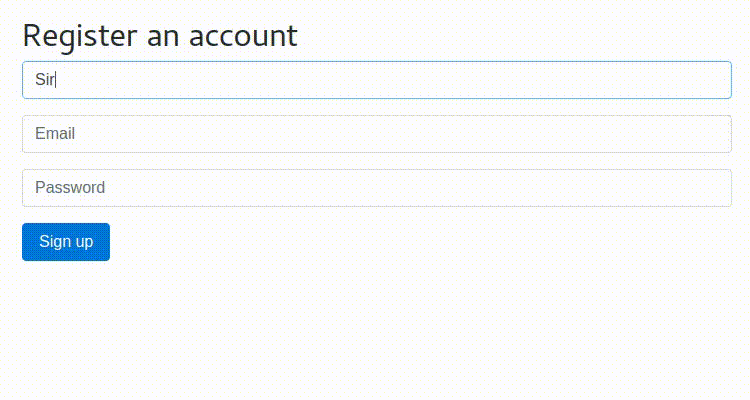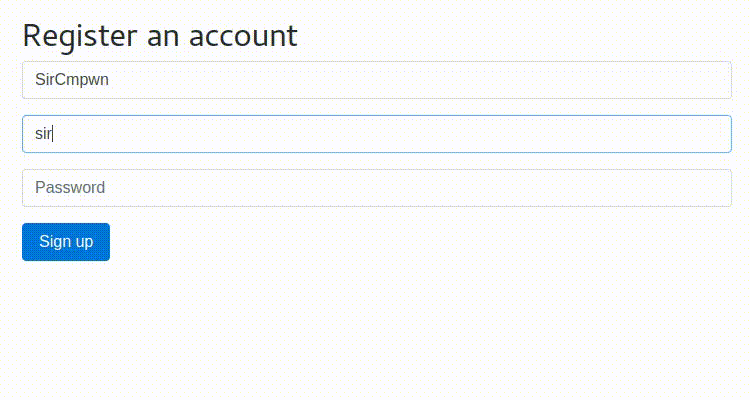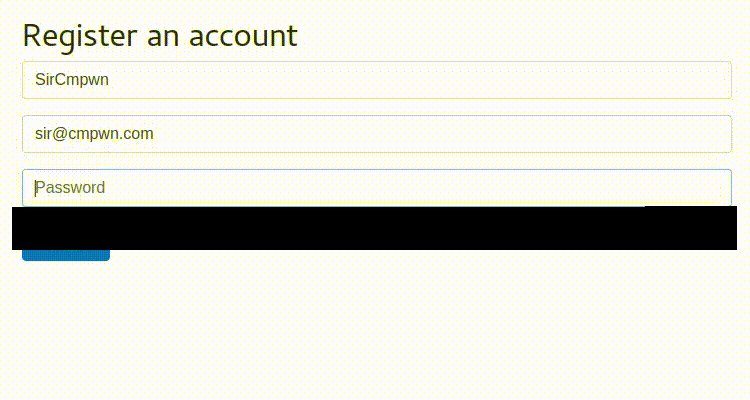
evilpass
Checks how strong your user's password is via questionably ethical means.
Drew DeVault -
Against DNSSEC
All secure crypto on the Internet assumes that the DNS lookup from names to IP addresses are insecure. Securing those DNS lookups therefore enables no meaningful security. DNSSEC does make some attacks against insecure sites harder. But it doesn’t make those attacks infeasible, so sites still need to adopt secure transports like TLS. With TLS …
-
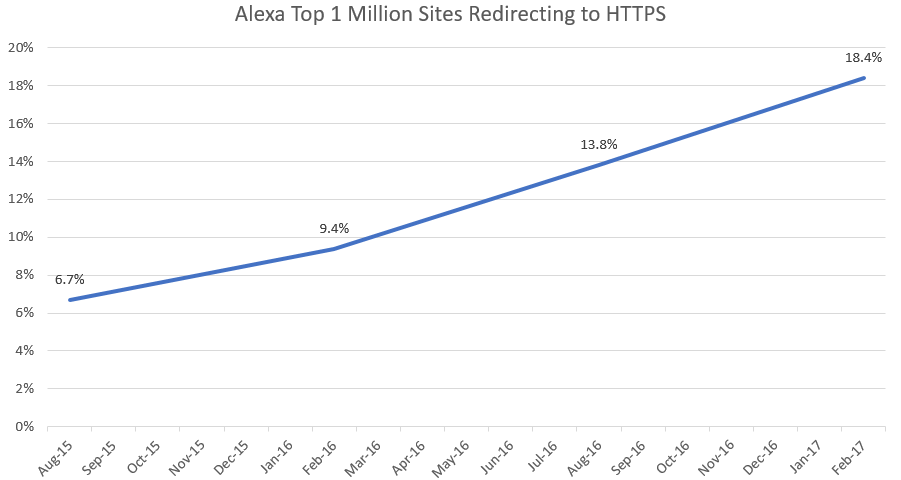
Troy Hunt: HTTPS adoption has reached the tipping point
That's it - I'm calling it - HTTPS adoption has now reached the moment of critical mass where it's gathering enough momentum that it will very shortly become "the norm" rather than the exception it so frequently was in the past. In just the last few months, there's been some really significant things happen that …
-
NISTs new password rules what you need to know
It’s no secret. We’re really bad at passwords. Nevertheless, they aren’t going away any time soon.
With so many websites and online applications requiring us to create accounts and think up passwords in a hurry, it’s no wonder so many of us struggle to follow the advice of so-called password security experts.
At the same time, the … -
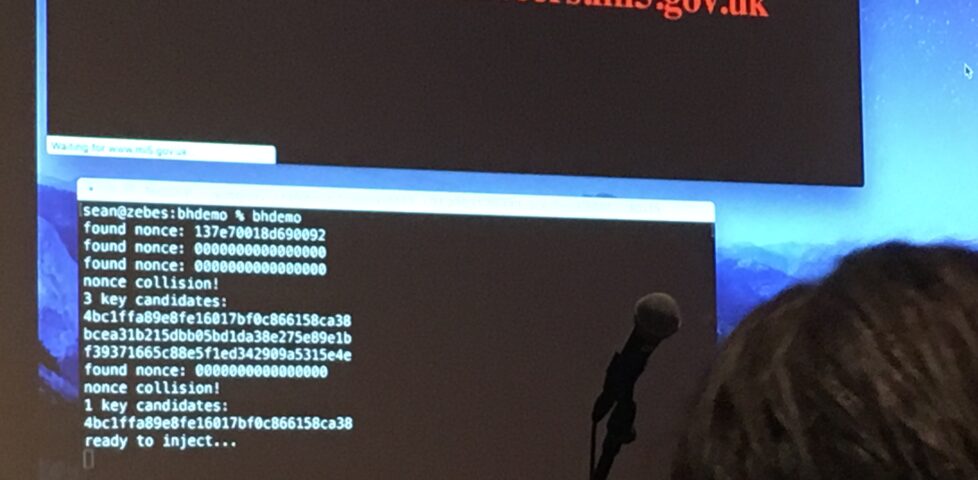
Breaking https' AES-GCM (or a part of it)
The coolest talk of this year's Blackhat must have been the one of Sean Devlin and Hanno Böck. The talk summarized this early year's paper, in a very cool way: Sean walked on stage and announced that he didn't have his slides. He then said that it didn't matter because he had a good idea …
-
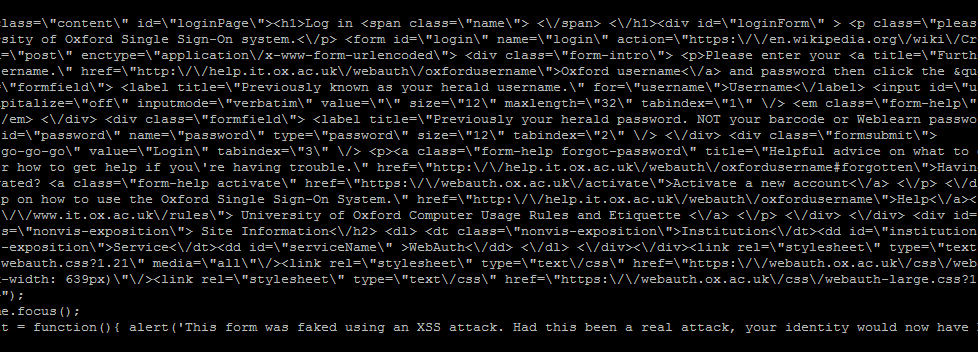
Anatomy of Cookie XSS
Using a real-life vulnerability he discovered on the University of Oxford's IT Services website as an example, Dan reminds you of the importance of sanitising even cookie data to prevent XSS vulnerabilities.
-
Payment Redirection Fraud
Here is an example scenario You receive an email requesting a payment. It could be for rent, it could be fees for a course or any other legitimate reason. Typically, the payment is a significant sum. The email contains the banking details you need to make the payment. Then shortly after the 1st email arrives…
… -
Raspberry Pi VPN Hotspot (or How To Infuriate Theresa May For Under £40)
For a small sum of money and a little time, you too can have a little box that encrypts everything on your WiFi network until it leaves the UK.
-
Squiz CMS Easter Eggs (or: why do I keep seeing Greg's name in my CAPTCHA?)
When using the Squiz CMS, Dan noticed that his CAPTCHA kept containing the same patterns of letters. These turned out to be the names of early developers on the system, which in turn lead Dan to uncover Easter Eggs in the software that have been deliberately concealed by their authors.
-
Social Engineering of the Day
Dan goes to deliver a lecture on security and, before he's even identified himself, manages to find out from the receptionist the best way to circumvent their door locks.
-
Something like HTTPS Everywhere for new Opera?
I'm looking for an extension that will automatically redirect-to-HTTPS for particular domains, e.g. to ensure that I'm using the secure version of Wikipedia, etc., whenever I go there. The HTTPS Everywhere plugin from the EFF does this for Firefox and Chrome; what can I do to make this work in Opera?
-
Phone Security == Computer Security
Dan gets paranoid and despairs about the ease with which mobile devices can be stolen, the wealth of personal information stored on them, and the under-use of readily-available encryption tools.
-
Rave Reviews for Your Password Sucks
After running a breakout session entitled "Your password: how bad guys will steal your identity" at the 2012 UAS Conference, Dan gets rave reviews. Nice.
-
KeePass for Opera
Dan develops a browser plugin for Opera to allow the KeePass Password Safe to work with Opera 12+, after the Opera team remove the feature upon which many KeePass users depended.