Tag: web
-
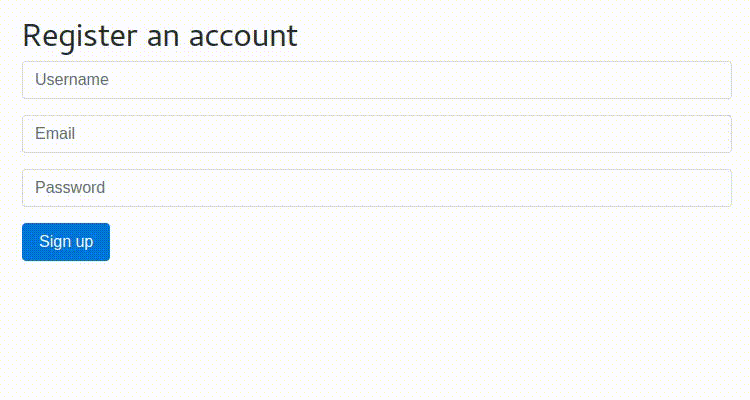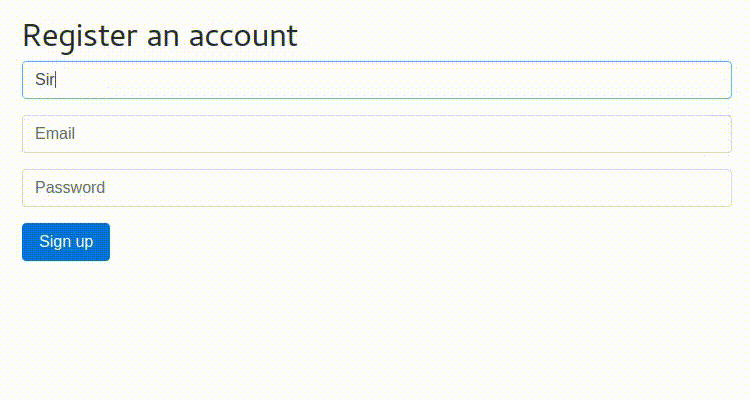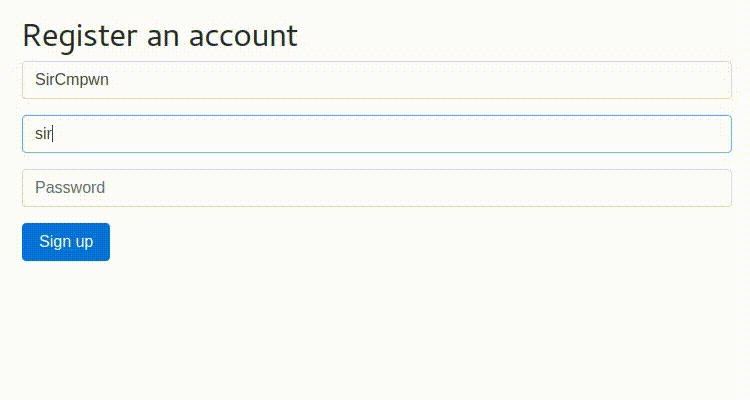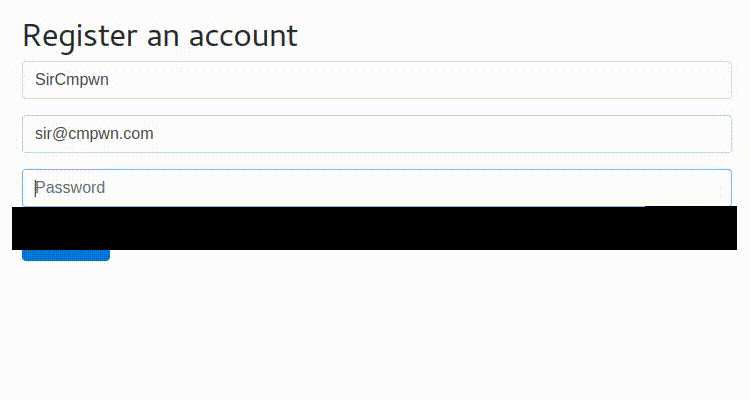
evilpass
Checks how strong your user's password is via questionably ethical means.
Drew DeVault -
Against DNSSEC
All secure crypto on the Internet assumes that the DNS lookup from names to IP addresses are insecure. Securing those DNS lookups therefore enables no meaningful security. DNSSEC does make some attacks against insecure sites harder. But it doesn’t make those attacks infeasible, so sites still need to adopt secure transports like TLS. With TLS …
-
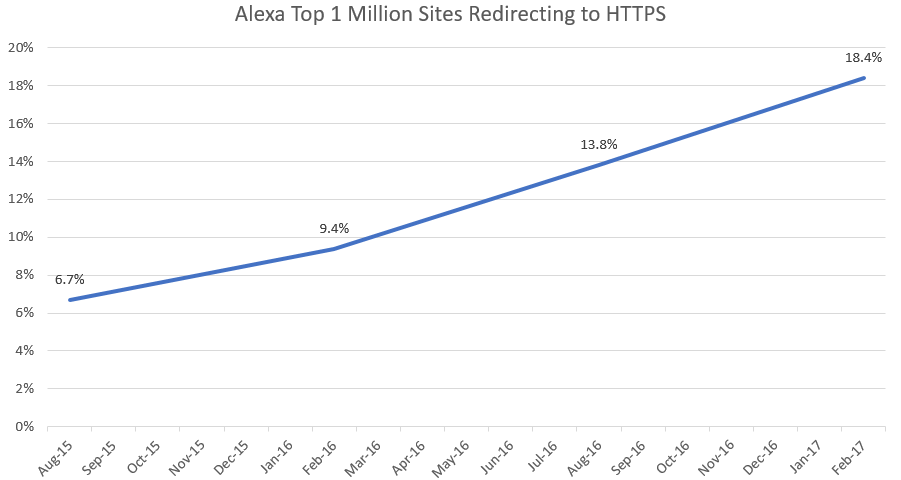
Troy Hunt: HTTPS adoption has reached the tipping point
That's it - I'm calling it - HTTPS adoption has now reached the moment of critical mass where it's gathering enough momentum that it will very shortly become "the norm" rather than the exception it so frequently was in the past. In just the last few months, there's been some really significant things happen that …
-
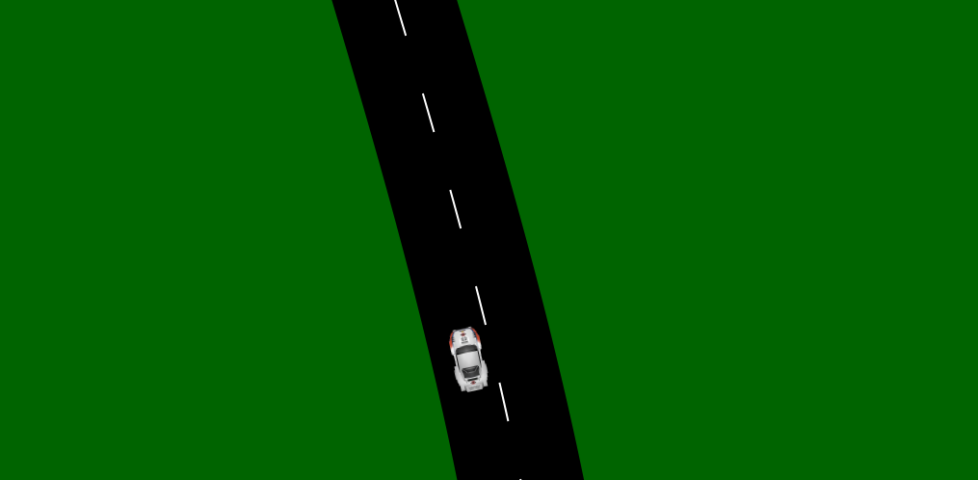
Steer! An Experimental Canvas/Websocket Game
Left alone to look after a conference stand, Dan implements a browser-based video game prototype called Steer! in which the player uses their mobile phone to control a speeding car.
-
Tomorrow's Web, Today
Feeling optimistic about the technical future of the Web, Dan finds the opportunity to hack about with some promising new tools: Intersection Observers, Web Workers, Blobs, and the Fetch API.
-
Things you probably didnt know you could do with Chromes Developer Console
Chrome comes with built-in developer tools. This comes with a wide variety of features, such as Elements, Network, and Security. Today, we’ll focus 100% on its JavaScript console.
When I started coding, I only used the JavaScript console for logging values like responses from the server, or the value of variables. But over … -
Pornhub Bypasses Ad Blockers With WebSockets
Pornhub has found an innovative way to deliver ads to users of ad blocking software, exploiting limitations in Chrome’s content blocking API...
BugReplay -
History of the browser user-agent string
In the beginning there was NCSA Mosaic, and Mosaic called itself NCSA_Mosaic/2.0 (Windows 3.1), and Mosaic displayed pictures along with text, and there was much rejoicing...
WebAIM
Have you ever wondered why every major web browser identifies itself as "Mozilla"? Wonder no longer... -
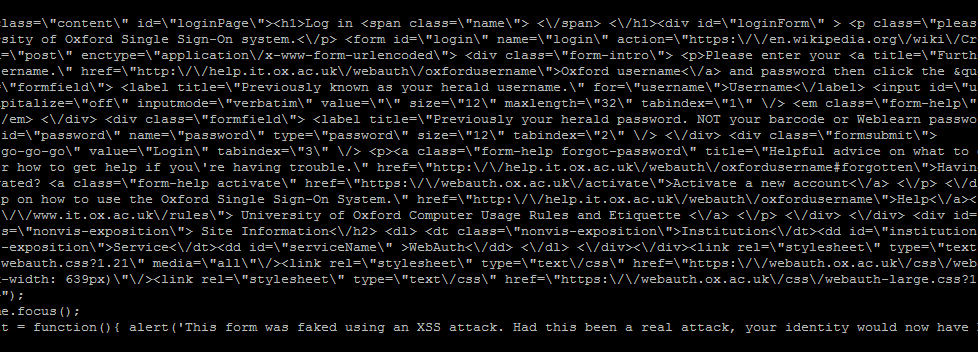
Anatomy of Cookie XSS
Using a real-life vulnerability he discovered on the University of Oxford's IT Services website as an example, Dan reminds you of the importance of sanitising even cookie data to prevent XSS vulnerabilities.
-
DRY: Do Repeat Yourself
I am increasingly of the opinion that the general software engineering adage “Don’t Repeat Yourself” does not always apply to web development. Also, I found that web development classes in CS academia are not very realistic. These two problems turn out to have the same root cause: a lack of appreciation of what browsers do…
… -
Zopfli Optimization: Literally Free Bandwidth
In 2007 I wrote about using PNGout to produce amazingly small PNG images. I still refer to this topic frequently, as seven years later, the average PNG I encounter on the Internet is very unlikely to be optimized.
For example, consider this recent Perry Bible Fellowship cartoon...
Jeff Atwood -
Non-Rails Frameworks in Ruby: Cuba, Sinatra, Padrino, Lotus
It’s common for a Ruby developer to describe themselves as a Rails developer. It’s also common for someone’s entire Ruby experience to be through Rails. Rails began in 2003 by David Heinemeier Hansson, quickly becoming the most popular web framework and also serving as an introduction to Ruby for many developers.
Rails is great. I use … -
Squiz CMS Easter Eggs (or: why do I keep seeing Greg's name in my CAPTCHA?)
When using the Squiz CMS, Dan noticed that his CAPTCHA kept containing the same patterns of letters. These turned out to be the names of early developers on the system, which in turn lead Dan to uncover Easter Eggs in the software that have been deliberately concealed by their authors.
-
Something like HTTPS Everywhere for new Opera?
I'm looking for an extension that will automatically redirect-to-HTTPS for particular domains, e.g. to ensure that I'm using the secure version of Wikipedia, etc., whenever I go there. The HTTPS Everywhere plugin from the EFF does this for Firefox and Chrome; what can I do to make this work in Opera?
-
Craziest Internet Explorer Bug Ever?
Dan discovers a crazy little bug in Internet Explorer 8 and below, and complains loudly about it. Bloody IE.