Tag: cookies
-
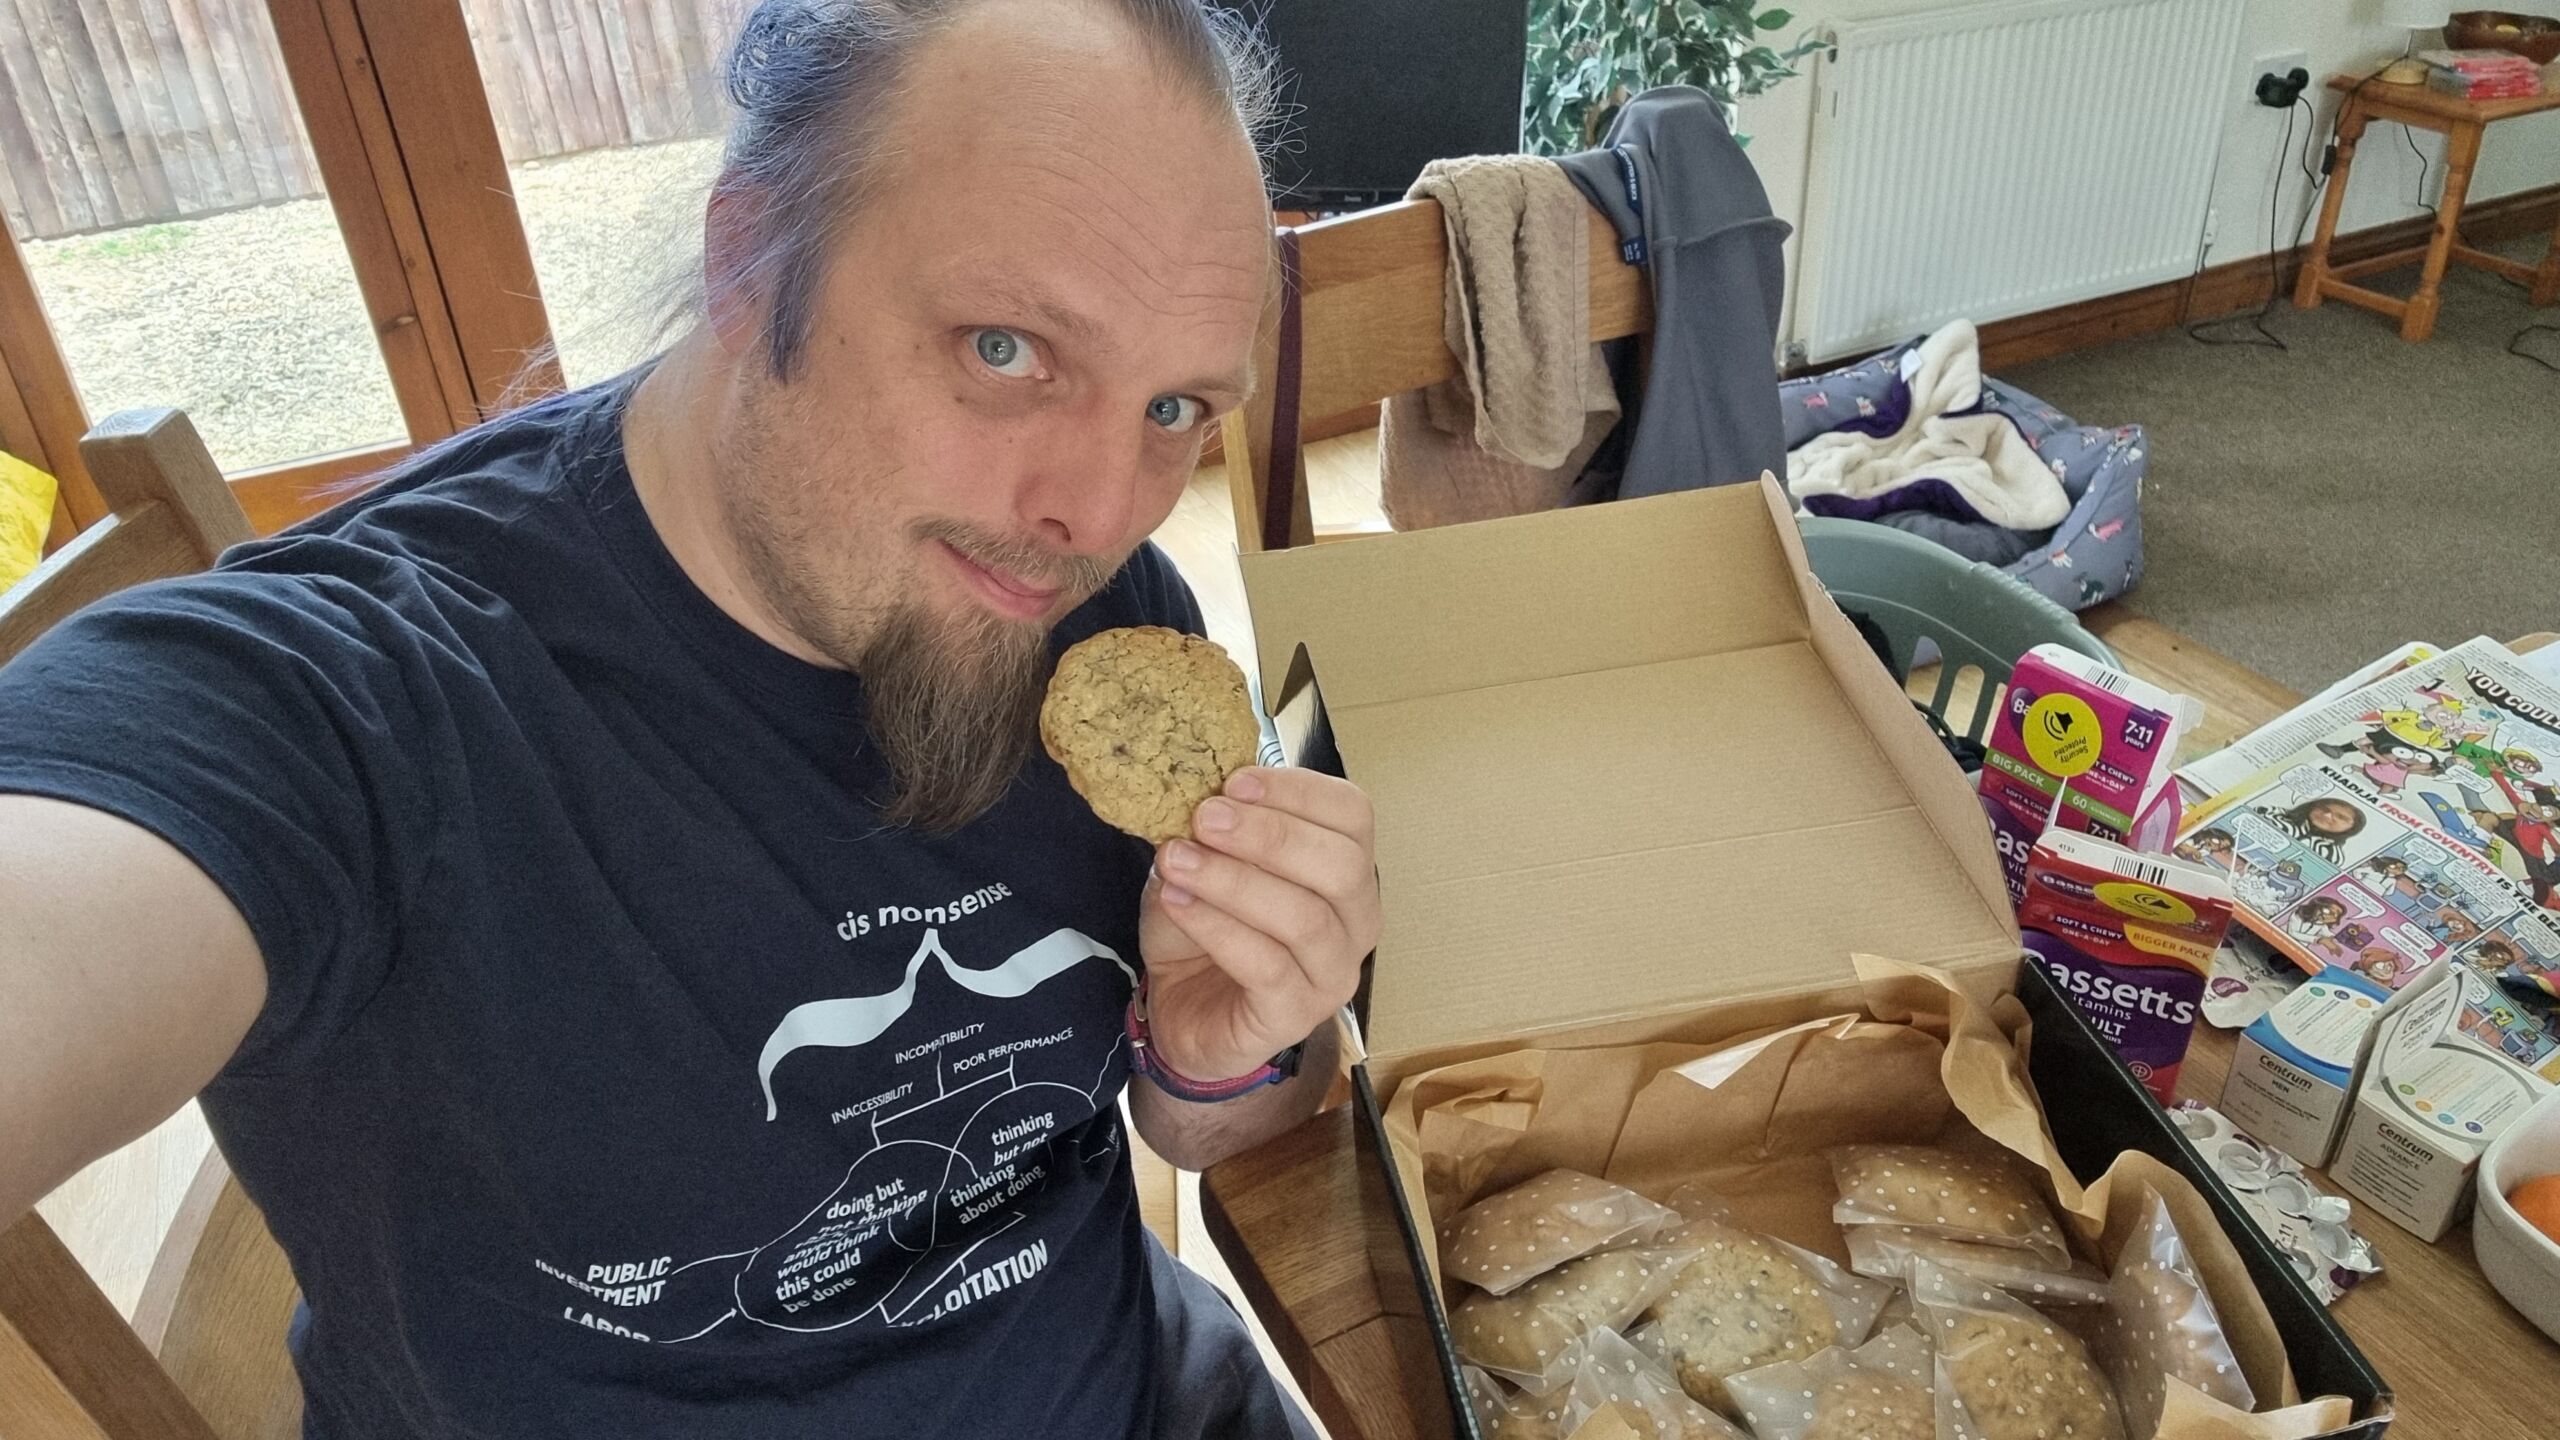
In sympathy for our flood situation, my sister baked and posted us a big batch of her fantastic raisin & oatmeal cookies.
Alt
Dan, a white man with a goatee beard and blue hair, sits next to a large box of cookies, about to eat one.
I've eaten like six of them already. Turns out I stress-eat. Who knew?
-
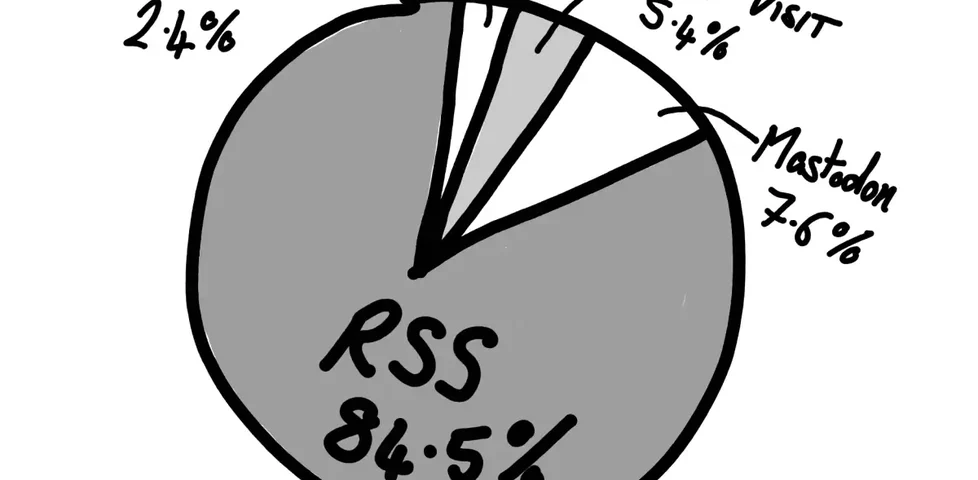
How You Read My Content (The Answers)
Kev Quirk ran a one-question survey recently about how people discover and read his blog posts, and I think it's a pretty inspiring idea. Sure, consent-based surveying introduces biases... but what analytic technique doesn't, really?
-
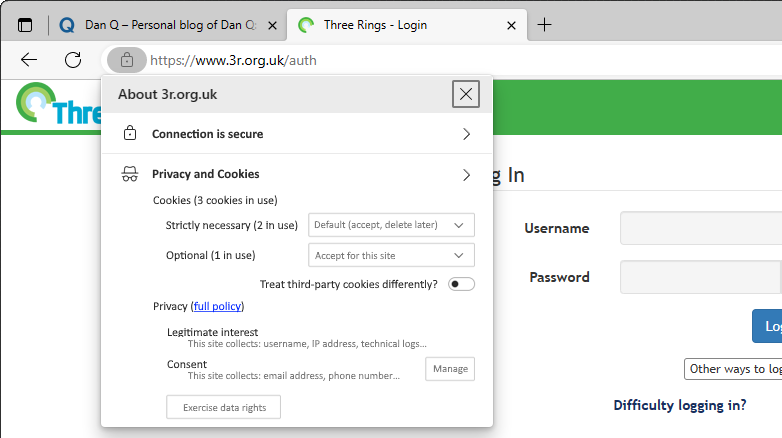
How a 2002 standard made 2022 bearable
Somewhere, in another timeline, the P3P standard is alive and thriving and saving us from cookie/privacy popovers.
-
Third party
Jeremy Keith wonders if the Web would have third-party cookies and JS at all if it were invented today, and Dan weighs in.
-
Just accepted @Facebook's new cookie policy. 😋 @USENIXSecurity #usesec19
-
"Stop Thinking About Consent: It Isn’t Possible and It Isn’t Right"
For a philosopher, Helen Nissenbaum is a surprisingly active participant in shaping how we collect, use, and protect personal data. Nissenbaum, who earned her PhD from Stanford, is a professor of information science at Cornell Tech, New York City, where she focuses on the intersection of politics, ethics, and values in technology and digital media …
-
Visitor Tracking Without Cookies (or How To Abuse HTTP 301s)
A technique for abusing HTTP 301 redirects and random numbers to uniquely track users; even those who have cookies disabled in their web browsers.
-
Leading By Example
After getting thoroughly confused by the new European Union directives on the use of cookies, which come into force later this month, Dan goes to the Information Commissioner's website to look for some guidance... only to discover that they don't meet the new requirements, either.
-
HttpOnly Session Cookies using ActiveRecordStore in Rails 2.2
If you're using CookieStore to manage sessions in your Ruby on Rails application, Rails 2.2 provides the great feature that you're now able to use HTTPOnly cookies. These are a great benefit because, for compatible web browsers, they dramatically reduce the risk of a Cross Site Scripting (XSS) attack being able to be used to …